
Phishing simulation for companies
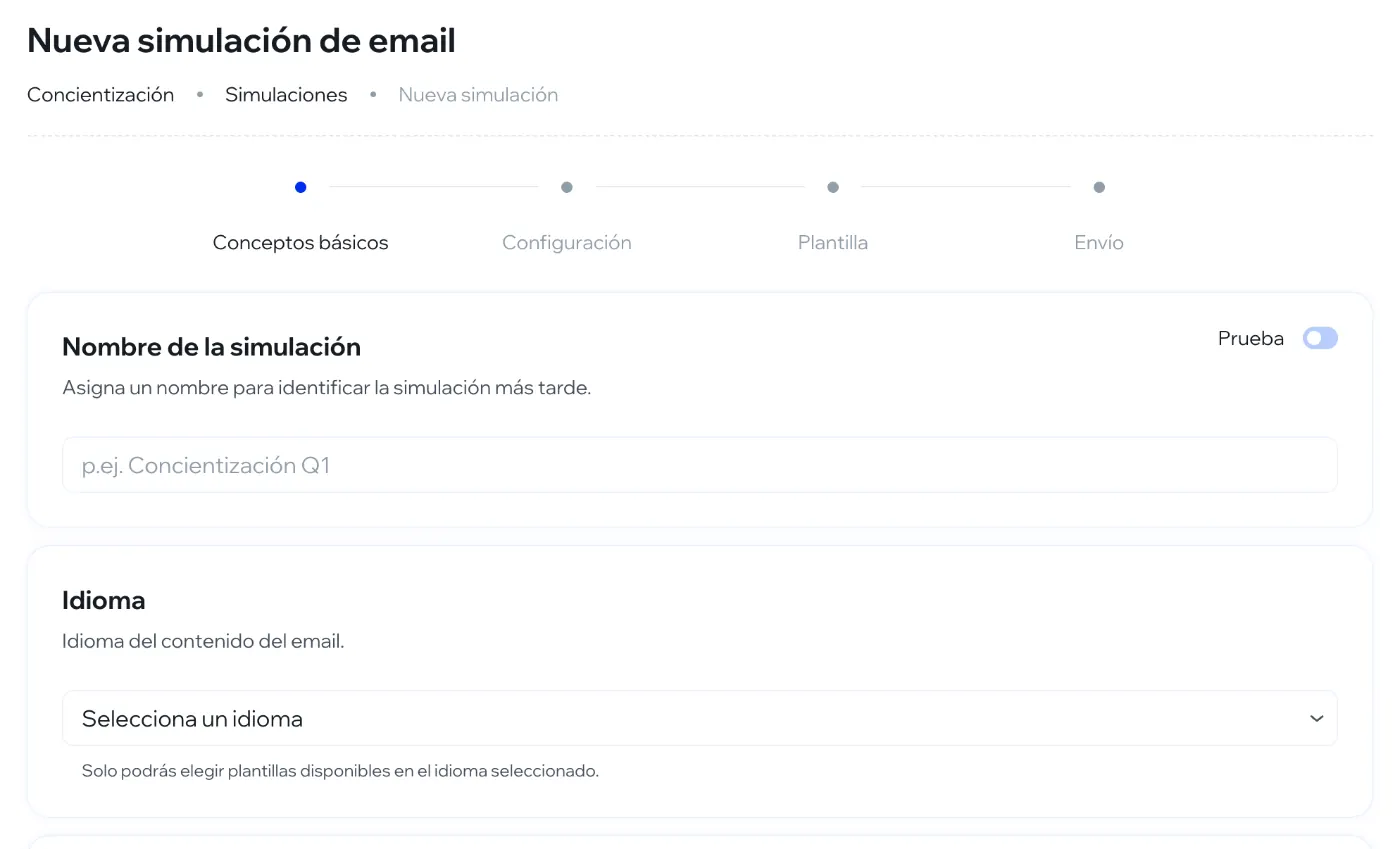
Native email phishing and QRishing, tailored to each risk profile. Each fail triggers training. Smishing and vishing run as a professional service.
How does a phishing simulation work?
Analyzes
The Agent evaluates each user's history and behavior to determine their level of exposure.
Simulates
Launches the right campaign for that profile: channel, scenario, and difficulty adjusted individually.
Intervenes
If the user falls for it, activates immediate training contextualized to the specific error made.
The mistake becomes a lesson, right there
Anyone who falls for a simulation doesn't get a scolding: they get a 3-minute micro-lesson that explains the trick while they still remember it.
Can you find the 5 signals?
This is a real email used in our simulations. Hover the marked areas and learn to read phishing the way an analyst does.
Dear team member,
We found an inconsistency in your August payslip. To avoid delays in the transfer, verify your bank details within the next 2 hours
Access the portal from this link: payroll-portal.company-online.net
Regards,
Human Resource Department
Five signals a phishing email usually carries together
The exercise is recognising the pattern. We do not publish a campaign rate.
What is native and what runs as a service?
phishing
Native email campaigns, adjusted to each user's risk profile, with difficulty based on history.
Native QR-code simulations. The QR jumps to the phone; the mail filter does not see it as a link.
modalities
Click-only, credential capture and ransomware by attachment. Three depths of the same email channel, not three products.
services
Smishing, vishing, USB drop, 2FA attacks and deepfake are not builder buttons. They run as a service, with scope and a report.
phishing
Native email campaigns, adjusted to each user's risk profile, with difficulty based on history.
Native QR-code simulations. The QR jumps to the phone; the mail filter does not see it as a link.
modalities
Click-only, credential capture and ransomware by attachment. Three depths of the same email channel, not three products.
services
Smishing, vishing, USB drop, 2FA attacks and deepfake are not builder buttons. They run as a service, with scope and a report.
phishing
Native email campaigns, adjusted to each user's risk profile, with difficulty based on history.
Native QR-code simulations. The QR jumps to the phone; the mail filter does not see it as a link.
modalities
Click-only, credential capture and ransomware by attachment. Three depths of the same email channel, not three products.
services
Smishing, vishing, USB drop, 2FA attacks and deepfake are not builder buttons. They run as a service, with scope and a report.
Actionable visibility, not just click rate
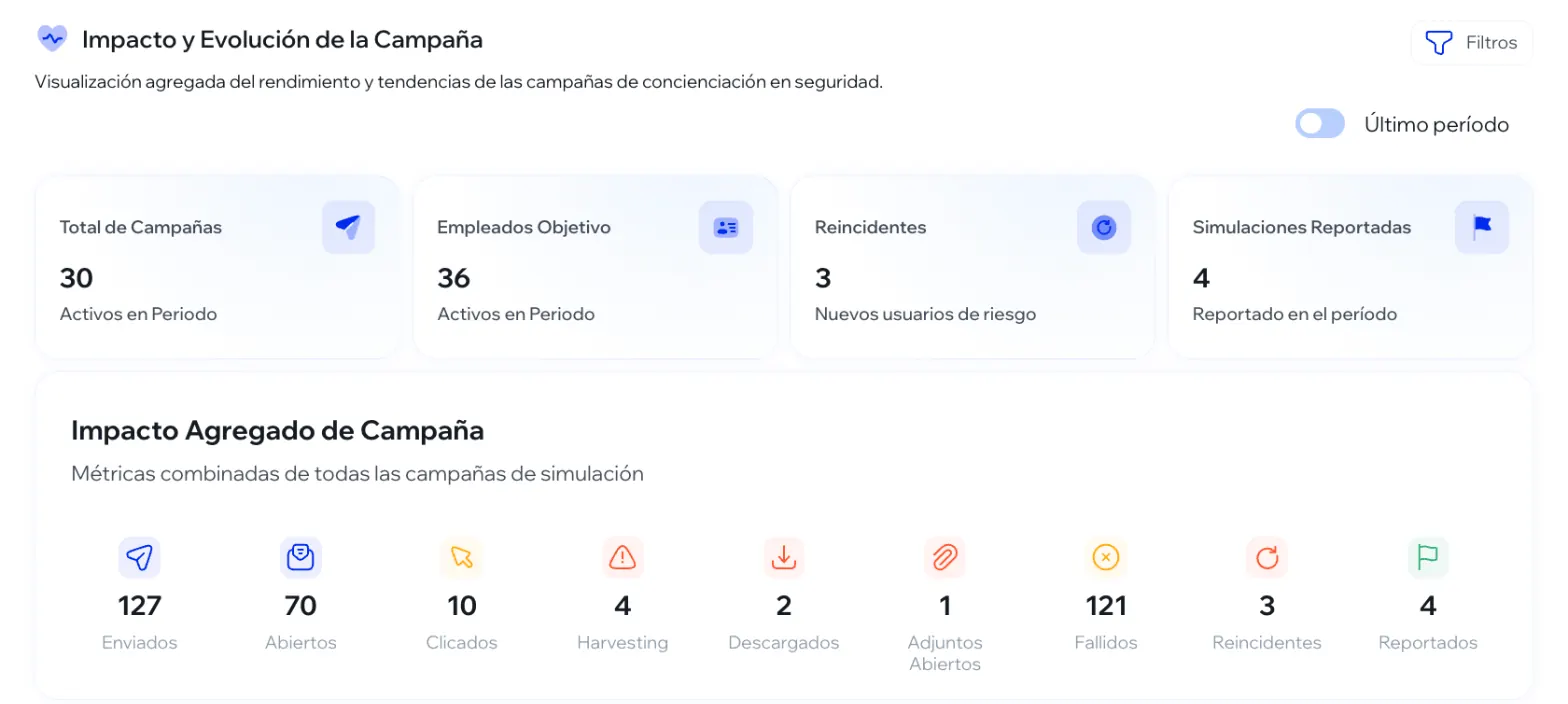
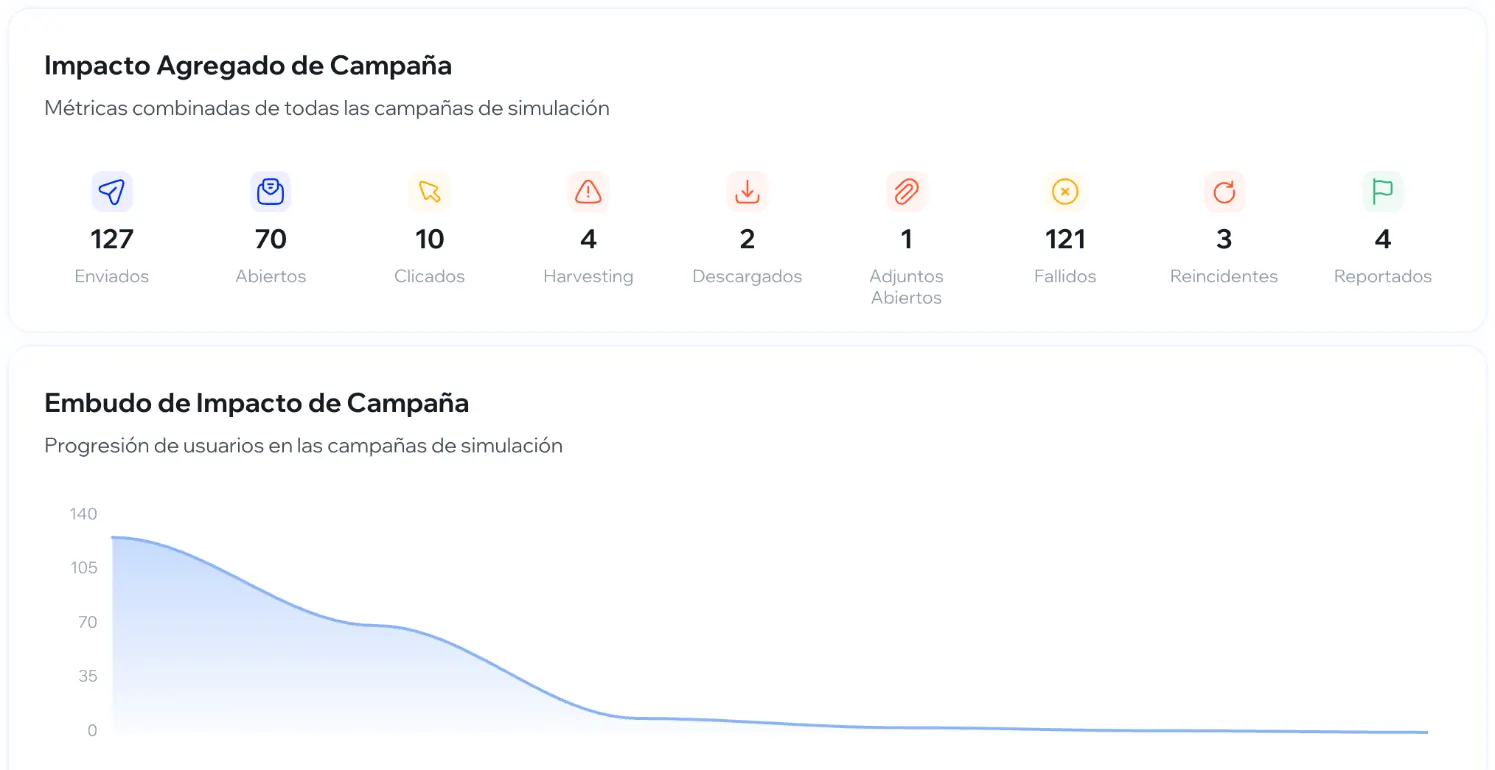
Every campaign generates behavioral data to understand real exposure, prioritize interventions, and demonstrate evolution.
Click rate by user, team and organization Report rate: who detected and reported the threat before falling Evolution: how the risk profile improves over time
Simulations for the real world
Executive fraud, credential theft, fake vendors, compromised access. Whalemate replicates the most frequent attack vectors with templates by industry, role, and operational context — designed to replicate what your teams face day to day.
What does public data say about phishing?
Third-party figures, each with its source. Each customer’s results stay in their platform. Reviewed on October 28, 2026.
| Figure | What it says | Source |
|---|---|---|
| 62% | of breaches involved a human element; social engineering was the third most common pattern, at 16%. | Verizon DBIR 2026 |
| 16% and 6% | of breaches started with phishing and with pretexting, respectively. | Verizon DBIR 2026 |
| 1.4% vs. ~2% | median click rate in email simulations versus phone or text message: 40% higher on mobile channels. | Verizon DBIR 2026 |
| 21 s + 28 s | median time from opening the email to clicking, and from the click to entering data: under a minute. | Verizon DBIR 2024 |
| 20% | of users reported phishing in simulations; among those who clicked, 11% also reported it. | Verizon DBIR 2024 |
| 33.2% → 4.2% | users who fall for a phishing simulation before training and after one year of simulations and training, across 14.8 million users. | KnowBe4, 2026 report |
| 12.6.3.1 and 5.4.1 | PCI DSS v4.0.1 requires phishing and social engineering training and, separately, technical controls against phishing: meeting one does not meet the other. | PCI SSC, SAQ D |
How this module is used
Program capabilities
- Modalities
Click-only, credentials and ransomware
Three modes of the same campaign: measure the click, the hand-over of data, or the ransomware gesture. The library classifies them. Not three separate products.
- Landing
Post-fail landing
The screen whoever falls sees. It measures the gesture — open, hand over, execute — without being a customer microsite or a form that asks for a real secret.
- Calendar
Launch calendar
When each campaign goes out. The annual plan lives with the analyst; here you see the cadence so the roster is not flooded and months are not left silent.
- Reinforcement
Automatic enrollment after a fail
Whoever falls enters the course for that error. The simulation fires; training assigns. Reinforcement does not wait for the quarterly pack.
Phishing simulation for companies: email, QRishing and three modes
Campaigns adapt to the profile, not to a monthly blast. We do not publish customer click rates or unsourced averages. We publish the criterion: channel, difficulty, and what happens after the error.
A phishing simulation that works measures behavior; it does not produce a ranking for a photo. The payroll email and the store QR exist because the real attack uses those native channels. The Agent picks difficulty and frequency from history. Treasury and the sales floor do not get the same lure on the same Tuesday. If the person falls for it, the cycle continues in contextual training. If they do not, the bar can rise. The security team sets rules. It stops slicing lists.
Adaptive phishing covers email. QRishing covers the scan gesture — not a PDF about codes. Three modes on the same email channel: click-only, credential capture and ransomware by attachment. Smishing, vishing, USB drop, 2FA attacks and deepfake run as professional services, not as builder buttons. Here we do not sell a pack with an improvement percentage. We declare what is native and what is measured: exposure and habit, not a loose rate.
What we do not do matters as much as the catalog. We do not publish customer click rates or a “LATAM average.” We do not use the result for a file. We do not install an endpoint agent to “see the click.” The simulation is a controlled exercise. The report says what happened in that campaign. The index accumulates the signal. Leadership sees evolution, not a hall of shame. If someone quotes you a program with a click rate printed on the cover, ask where the number came from.
Questions about phishing simulation
Which channels does a native phishing simulation cover?
What is the typical click rate?
What happens when someone falls for it?
Do templates look like our flows?
Do smishing, vishing, or deepfake come in every plan?
Measure your response to real threats
Book a demo and see how Whalemate designs simulations adapted to each user's risk profile.
Updated